Security before generation
RAG systems leak if authorisation is checked after retrieval. The design enforces policy inside the retrieval boundary so forbidden content never enters the model context.
Enterprise document intelligence with retrieval-augmented generation.
Professional work on a confidential enterprise system. Details abstracted; no client UI, data or implementation specifics are shown.
01
Enterprises accumulate documents faster than people can find the relevant fragment. Reports, policies and historical decisions sit across systems, and answering a concrete question often means manually reading for hours.
A naive chatbot over documents is not enough: access control, document timeframes and organisational authorisation all determine who should see what — and wrong disclosure is worse than no answer.
02
Professional engagement on a confidential enterprise document management and reporting system. Specific client, UI, data and architectural details are not disclosed.
This page intentionally stays at system-concept level: it explains the shape of the problem and the approach without exposing confidential implementation.
03
04
A retrieval layer that selects documents the requesting user is authorised to see, filtered by timeframe and access policy before generation ever runs.
RAG over curated corpora so answers cite source material instead of improvising, with structured report outputs for decision-support workflows.
Human-in-the-loop review paths: the system proposes, people decide — appropriate for enterprise document contexts where errors have consequences.
06
07
Authorisation is enforced in the retrieval path, not as a prompt instruction — the model only ever sees documents the user is allowed to access.
Document metadata (effective dates, supersession, classification) is first-class, so timeframe questions return historically correct material rather than only latest revisions.
Generation is constrained to retrieved context with citations, and outputs are structured for decision-support review rather than free-form chat.
Concrete technologies, vendors, volumes and interfaces remain confidential and are deliberately omitted from this case study.
08 / Hard parts
RAG systems leak if authorisation is checked after retrieval. The design enforces policy inside the retrieval boundary so forbidden content never enters the model context.
Enterprise questions are often 'what was true then?' — not 'what is true now?'. Making document time validity a retrieval dimension, not a post-filter, was essential.
Explaining a system you cannot fully show forces precision: abstract diagrams, honest context labels and clear role statements instead of screenshots that cannot exist publicly.
09
A confidential enterprise system in active professional use, covering document intelligence, authorised retrieval and decision-support reporting. Specific outcomes, volumes and client identifiers are not disclosed. This case study documents the problem shape and engineering approach only.
10
Evidence
Private
Implementation and client details withheld
Case study
Abstract architecture and approach
Technology
11
.png)
AI-powered fire risk prediction and computer vision detection.
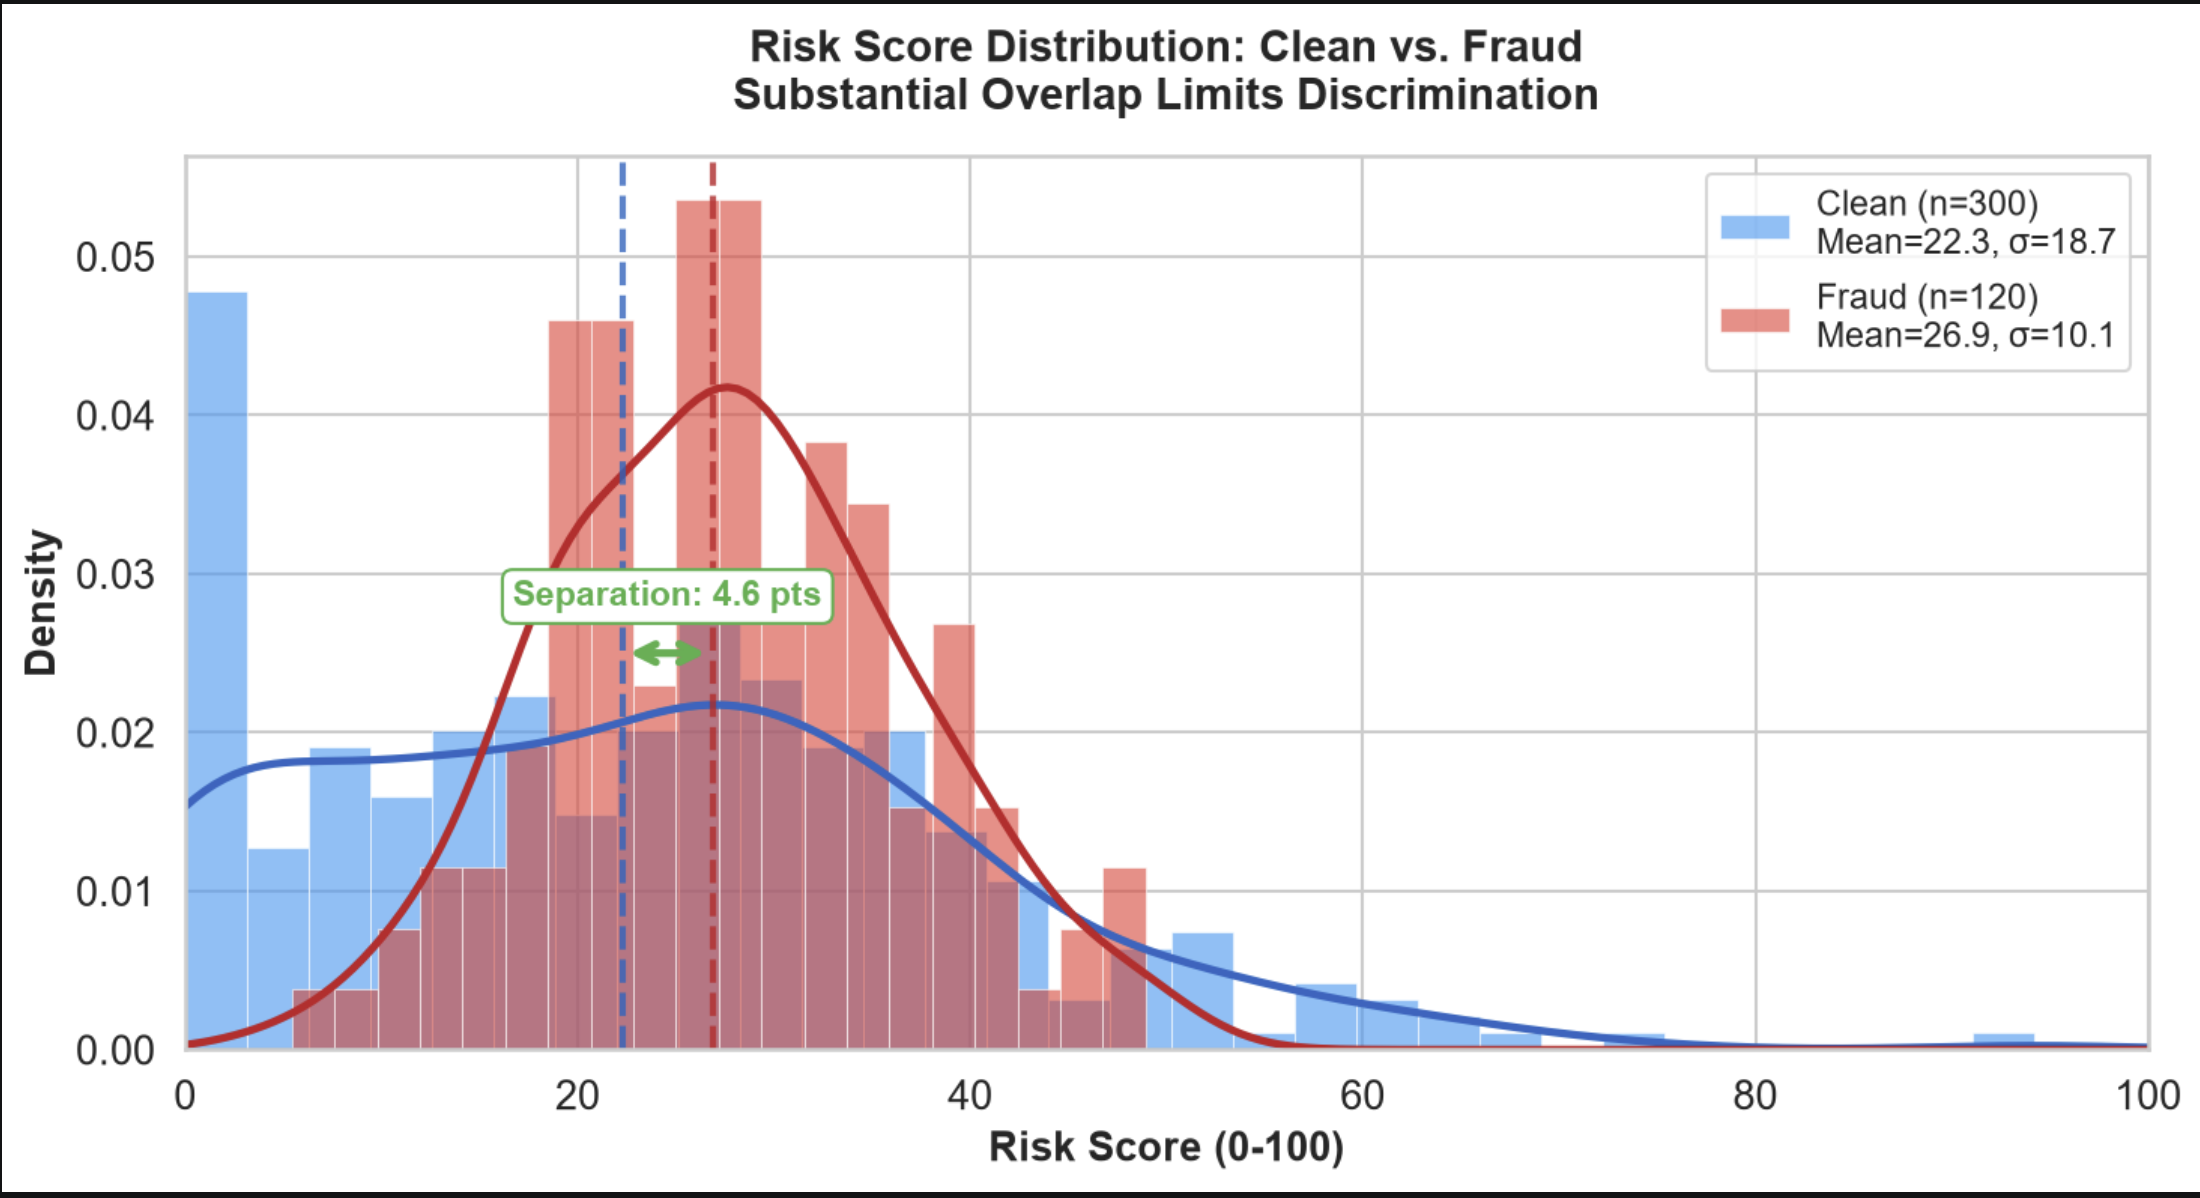
Anomaly detection and decision support for tax compliance and revenue assurance.
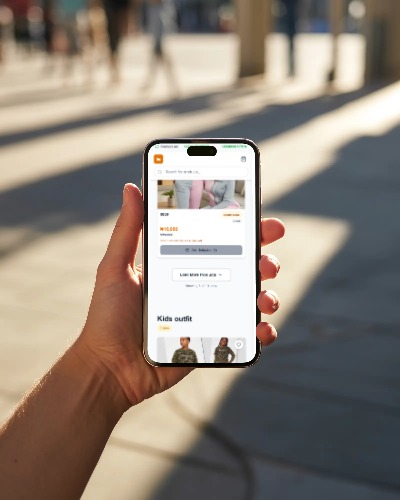
Commerce platform for product discovery through checkout.
Start a project
If this kind of system is close to your problem, tell us what you are trying to ship.